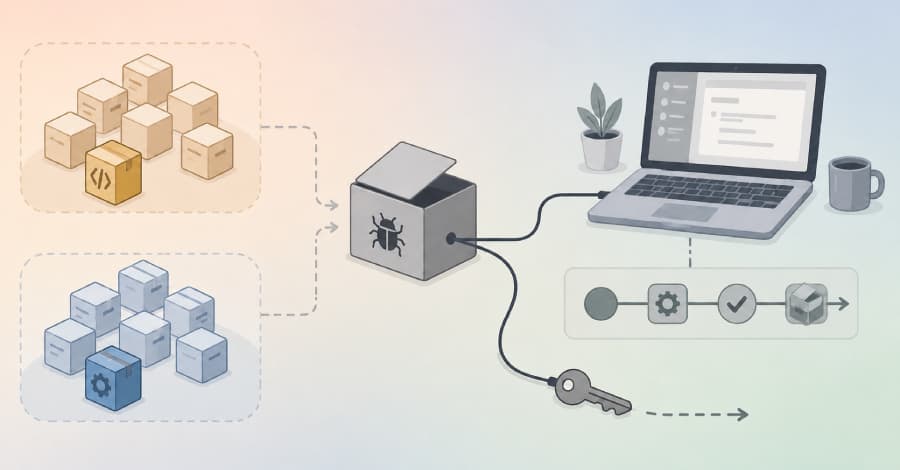
Cybersecurity researchers have flagged yet another evolution of the supply chain attack linked to the Mini Shai-Hulud, Miasma, and Hades malware family that has compromised a new set of npm packages, even as it has propagated to the Go ecosystem. "The latest activity includes malicious npm releases
Key Insights
10 editorial insights.
The recent discovery of Miasma malware targeting India's software supply chain through npm packages and GitHub underscores a significant escalation in supply chain attacks. This incident not only highlights vulnerabilities in widely-used package management systems but also raises concerns about the integrity of software dependencies that developers rely on daily.
Key players in this incident include GitHub and npm, both of which are integral to open-source development and software distribution. Their platforms serve millions of developers globally, and any compromise can have cascading effects, impacting a vast array of applications and services that depend on these resources.
This development is strategically important as it signals a shift in the tactics employed by cybercriminals, moving toward more sophisticated supply chain attacks. The ability to compromise trusted sources like npm and GitHub can undermine developer trust and lead to broader implications for software security practices across the industry.
For companies and developers, the business impact is profound; compromised software can lead to data breaches, operational disruptions, and significant financial losses. Additionally, end users may face privacy violations and the potential for identity theft, further eroding trust in software products.
This incident connects to a larger trend of increasing supply chain vulnerabilities observed over the past 12-24 months. As organizations transition to more agile and decentralized development practices, the risk of malicious code injection in widely-used libraries is growing, necessitating enhanced security measures.
The software security market, valued at approximately $4 billion in 2022, is expected to grow at a CAGR of around 10% through 2028. Incidents like the Miasma malware will likely accelerate investment in security tools and practices as organizations seek to mitigate risks associated with supply chain vulnerabilities.
The primary risks posed by this malware include potential data theft, unauthorized access to systems, and the propagation of malicious code within development environments. Unresolved questions remain regarding how many packages have been impacted and whether similar vulnerabilities exist across other ecosystems.
Competitors in the cybersecurity space will likely respond by enhancing their security offerings, focusing on supply chain risk management. Companies like Snyk and WhiteSource may capitalize on this incident by promoting their solutions that help developers identify and mitigate vulnerabilities in third-party components.
In the next 6-12 months, watch for regulatory milestones such as the introduction of stricter requirements around software supply chain security. Governments may impose guidelines that compel companies to adopt robust security practices, impacting how software is developed and distributed.
The bottom-line significance for technology professionals and investors is clear: as supply chain attacks become more prevalent, the demand for secure development practices will rise sharply. Investors should closely monitor cybersecurity firms and solutions that address these vulnerabilities, as they are likely to see increased adoption and growth in the coming years.
A new strain of malware, dubbed Miasma, has been identified targeting npm packages and GitHub Actions, heightening concerns over supply chain vulnerabilities. This development is particularly alarming as it showcases the growing sophistication of cyber threats in the software development lifecycle, making it crucial for developers and companies to bolster their security measures.
The Miasma malware operates by injecting malicious code into legitimate npm packages, which are then distributed through the ecosystem. This enables attackers to execute arbitrary commands and potentially compromise the systems of developers and companies that incorporate these packages into their projects. The integration with GitHub Actions allows for automated workflows to be hijacked, amplifying the impact of such attacks and making detection more challenging.
In the broader industry context, the rise of supply chain attacks is becoming a critical concern. With the increasing reliance on open-source software, platforms like npm face mounting pressure to secure their ecosystems. Recent reports indicate a significant uptick in attacks targeting software supply chains, revealing vulnerabilities that developers must address. The competition among software security firms is intensifying as organizations seek robust solutions to mitigate these risks.
In India, the tech ecosystem is not immune to the implications of Miasma. With a burgeoning community of developers and startups heavily reliant on npm packages, the threat poses risks to countless projects across sectors, including fintech, e-commerce, and health tech. Indian tech companies must prioritize security and educate their developers about safe coding practices to prevent falling victim to such malware.
Key Highlights
- Miasma malware exploits npm packages to execute remote commands.
- Targets GitHub Actions, complicating automated workflows.
- Supply chain attacks increased by over 300% in the last year.
- Companies with robust security protocols will mitigate risks best.
- Expect more stringent npm security measures in the coming months.
Real-World Impact
The immediate effects of the Miasma malware will be felt by developers and security teams in software companies. Job roles such as software engineers, DevOps professionals, and IT security experts will need to adapt to heightened security protocols and conduct thorough evaluations of their dependencies to safeguard their applications.
Why This Matters
This incident highlights a significant shift in the threat landscape, underscoring the need for organizations to rethink their security strategies. CTOs and developers should implement proactive measures, such as automated dependency scanning and regular security audits, to protect their software supply chains from similar attacks.
As Miasma continues to evolve, keeping abreast of emerging threats is essential for developers. One key area to monitor is the response from npm and GitHub regarding enhanced security protocols that may emerge in the wake of this incident.
Found this useful? Share it!