● LIVE
OpenAI releases GPT-5 APIIndia AI startup raises $120MBitcoin ETF hits record inflowsMeta Llama 4 benchmarks leakedOpenAI releases GPT-5 APIIndia AI startup raises $120MBitcoin ETF hits record inflowsMeta Llama 4 benchmarks leaked
📅 Thu, 15 Oct, 2026✈️ Telegram
AiFeed24

AI & Tech News

🔍
✈️ Follow
🏠Home🤖AI💻Tech🚀Startups₿Crypto🔒Security🇮🇳India☁️Cloud🔥Deals
✈️ News Channel🛒 Deals Channel
Home/Articles/#malware

Topic

#malware

26 articles found

Google Disables NetNut Proxy Network to Combat Malware Threats
· · ET Tech

Google Disables NetNut Proxy Network to Combat Malware Threats

The tech giant said it ‌disabled accounts ⁠and ⁠services used in NetNut-related malware command-and-control operations and shared technical intelligence on the ​group's infrastructure with law enforcement and industry partners to support broader enforcement ​efforts.

#google#netnut#malware#cybersecurity#india-specific
Umbrij Malware Exploit Exposes Gmail Accounts via OAuth Flaw
· · The Hacker News

Umbrij Malware Exploit Exposes Gmail Accounts via OAuth Flaw

The threat actor known as ToddyCat has been attributed to a new malware called Umbrij that's designed to gain surreptitious access to a victim's email correspondence via the Google API. "In this campaign, the attackers focused their attention on corporate email communications hosted on Gmail, target

#umbrij#malware#oauth vulnerability#gmail security#india cybersecurity
ChocoPoC RAT: New Threat Targets Vulnerability Researchers
· · The Hacker News

ChocoPoC RAT: New Threat Targets Vulnerability Researchers

Attackers are hiding a data-stealing trojan inside fake exploit code aimed at the people who hunt bugs for a living. The malware, called ChocoPoC, travels in Python proof-of-concept (PoC) repositories on GitHub that claim to exploit hot new CVEs. Run one, and it quietly lifts your saved passwords, b

#chocopoc rat#malware#cybersecurity#vulnerability researchers#india
· · Bleeping Computer

ChocoPoC Malware Targets Indian Researchers with PoC Exploits

Multiple weaponized proof-of-concept (PoC) exploits on GitHub were found delivering a Python-based remote access trojan (RAT) named ChocoPoC that can execute commands and steal sensitive data in a campaign believed to target cybersecurity researchers. [...]

#chocopoc#malware#cybersecurity#india#open-source
VEIL#DROP Malware Uses Blogger to Distribute PureLogs Stealer
· · The Hacker News

VEIL#DROP Malware Uses Blogger to Distribute PureLogs Stealer

Cybersecurity researchers have flagged a new multi-stage malware delivery attack chain that uses social engineering and Blogger pages to deliver an information stealer called PureLogs. The activity has been codenamed VEIL#DROP by Securonix. It's suspected that the initial payloads are distributed ei

#veil#drop#purelogs#malware#blogger#cybersecurity
ScreenConnect Exploited: AsyncRAT Attacks Target Users Globally
· · The Hacker News

ScreenConnect Exploited: AsyncRAT Attacks Target Users Globally

Unknown threat actors are leveraging the ScreenConnect remote access tool as a way to deploy and execute AsyncRAT. Kaspersky said the activity is part of a "massive, multi-domain, multi-language" campaign that distributes malicious installer archives hosted on spoofed websites. These installers masq

#screenconnect#asyncrat#cybersecurity#malware#india
API-Driven Malware Surge: Understanding ClickFix's Tactics
· · The Hacker News

API-Driven Malware Surge: Understanding ClickFix's Tactics

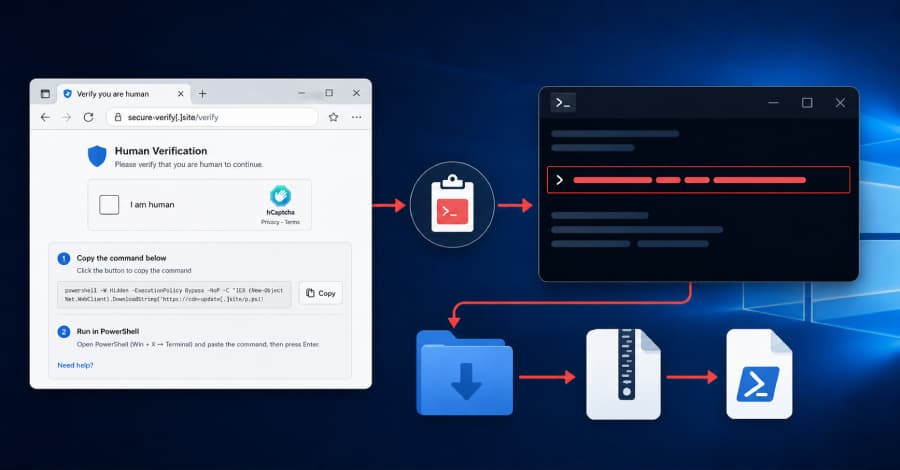
ClickFix, the trick that fools people into running malware by hand, has quietly grown a back office. New research shows the malicious commands behind its fake "prove you're human" pages are now handed out by API-driven servers that give each visitor the same malware in a different disguise. The same

#malware#clickfix#api-driven#cybersecurity#india-specific
Amazon Blocks Sideloading on Fire Stick Due to Malware Threats
· · Ars Technica AI

Amazon Blocks Sideloading on Fire Stick Due to Malware Threats

New Fire Stick OS helps Amazon block third-party homepage launchers, ad blockers.

#amazon#fire stick#sideloading#malware#india streaming
· · Graham Cluley

Chinese Malware Exploits USBs to Breach Japanese Military Networks

Read more in my article on the Hot for Security blog.

#malware#cybersecurity#military#usb attacks#india tech
India Faces New Malware Threat from CVE-2026-48558 Exploit
· · The Hacker News

India Faces New Malware Threat from CVE-2026-48558 Exploit

An unknown threat actor has been observed exploiting a recently disclosed maximum-severity security flaw in SimpleHelp to deliver two previously unreported malware families, TaskWeaver and Djinn Stealer. The intrusion involves the exploitation of CVE-2026-48558 (CVSS score: 10.0), a critical authent

#malware#cve-2026-48558#cybersecurity#india#remote support
· · SecurityWeek

Critical SimpleHelp Vulnerability Enables Malware Spread

The threat actor is focused on collecting credentials, SSH keys, cryptocurrency wallets, and development tooling. The post Critical SimpleHelp Vulnerability Exploited for Malware Delivery appeared first on SecurityWeek.

#simplehelp#malware#cybersecurity#remote access#india tech
Djinn Malware Threatens Cloud-AI Credentials: Here's What You Need
· · Dark Reading

Djinn Malware Threatens Cloud-AI Credentials: Here's What You Need

The infostealer was delivered via CVE-2026-48558, a critical authentication bypass vulnerability in SimpleHelp, targeting credentials linking development and admin environments to wider enterprise systems.

#djinn#malware#cloud security#ai vulnerabilities#india tech
· · Bleeping Computer

Critical SimpleHelp Vulnerability Exploited by New Djinn Stealer

Hackers are exploiting a recently disclosed critical vulnerability (CVE-2026-48558) in SimpleHelp to deploy Djinn Stealer, a previously undocumented cross-platform information stealer targeting Windows, macOS, and Linux. [...]

#simplehelp#djinn stealer#cybersecurity#malware#india
Microsoft Discovers and Disables 119 Malicious Edge Extensions
· · The Hacker News

Microsoft Discovers and Disables 119 Malicious Edge Extensions

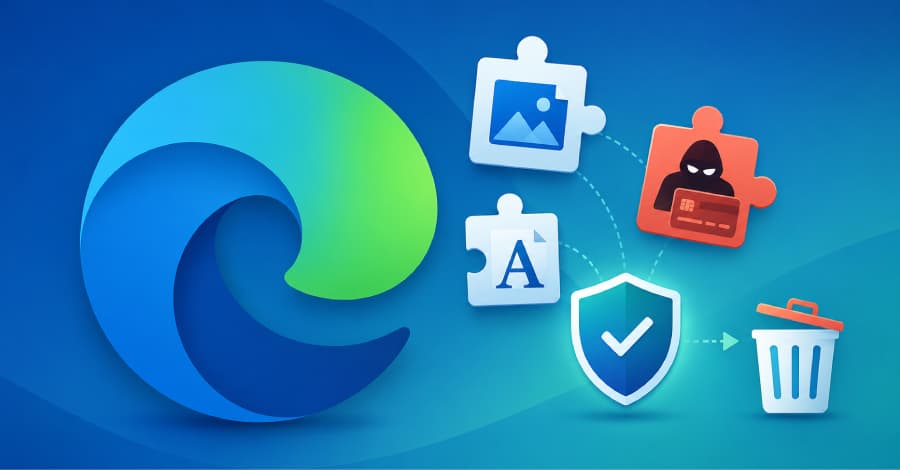
Microsoft has shut down a long-running malicious extension operation on the Edge Add-ons store that hid its payloads inside ordinary image and font files, then woke up days after install to steal credentials and run ad fraud. The company calls it StegoAd, a mash-up of steganography and adware, and t

#microsoft#edge extensions#malware#cybersecurity#india
WhatsApp Web Malware Alert: Essential Tips for Users
· · ET Tech

WhatsApp Web Malware Alert: Essential Tips for Users

The Indian Computer Emergency Response Team has warned WhatsApp web and desktop users to be cautious of any attachments, even if they come from a friend, colleague or family member.

#whatsapp#malware#cybersecurity#india#cert-in
· · Dev.to

Understanding the Promptware Kill Chain: New AI Threats Unveiled

https://www.youtube.com/watch?v=K68sqG18270&t=1s 提示词恶意软件杀伤链(The Promptware Kill Chain)。 传统的恶意软件(如勒索软件、间谍软件)通常是恶意代码,而 Promptware 则是一种全新的恶意软件执行模型,它是通过向生成式 AI 聊天机器人或智能体(Agent)输入恶意的“提示词”来驱动的。视频中引述了 Bruce Schneier 等人的研究,将这种攻击提炼为了一个完整的、步步渗透的“杀伤链”: 初始访问(Initial Access) [00:00:57] 直接注入:攻击者直接在对话框向 AI 输入指令,改变

#promptware#ai threats#cybersecurity#malware#india-specific
New SharkLoader Malware Threatens Cybersecurity with Cobalt Strike
· · The Hacker News

New SharkLoader Malware Threatens Cybersecurity with Cobalt Strike

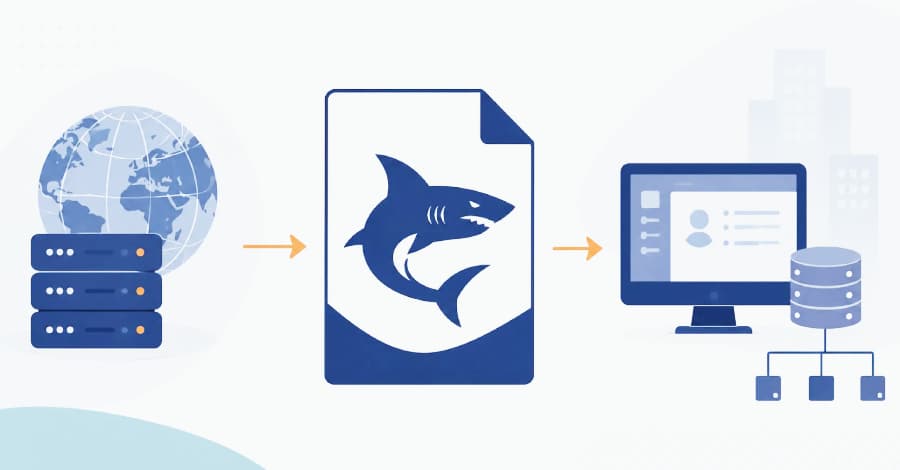
A newly discovered cyber attack campaign has been observed delivering a previously undocumented malware family called SharkLoader that acts as a loader for deploying Cobalt Strike Beacon on compromised hosts. Kaspersky, which is tracking the activity under the moniker StrikeShark, said the campaign

#sharkloader#cobalt strike#cybersecurity#malware#india cybersecurity
Gamaredon APT Escalates Threats: New Strategies Demanded
· · Dark Reading

Gamaredon APT Escalates Threats: New Strategies Demanded

The FSB state-sponsored operation has gotten a lot better at loading its malware and hiding its servers.

#gamaredon#apt#cybersecurity#malware#india cybersecurity
Europol Freezes $47M in Crypto Amid Malware Takedown
· · Decrypt

Europol Freezes $47M in Crypto Amid Malware Takedown

Police disrupted SocGholish, Amadey, and StealC, malware that harvests crypto wallets and passwords, freezing €41 million in crypto.

#europol#crypto#malware#cybersecurity#india-specific
· · Bleeping Computer

Malicious Edge Extension Exploits Native Messaging Loophole

A malicious Microsoft Edge extension dubbed 'Edgecution' has been used in a ransomware attack to escape the browser sandbox and deploy a Python-based backdoor. [...]

#edge extension#malware#security#india cybersecurity#browser vulnerabilities
Page 1 of 2Next →

🏷️ Popular Tags

#ai#technology#startups#crypto#security#india#cloud#mobile#machine-learning#chatgpt#openai#blockchain
AiFeed24

India's leading technology news platform. Delivering the latest in AI, startups, crypto and tech — curated daily by our editorial team.ews platform. Curated from 60+ trusted sources, curated by our editorial team.

✈️ @aipulsedailyontime (News)🛒 @GadgetDealdone (Deals)

Categories

🤖 Artificial Intelligence💻 Technology🚀 Startups₿ Crypto🔒 Security🇮🇳 India Tech☁️ Cloud📱 Mobile

Company

About UsContactEditorial PolicyAdvertiseDealsAll StoriesRSS Feed

Daily Digest

Top AI & tech stories every morning. Free forever.

Privacy PolicyTerms & ConditionsCookie PolicyDisclaimerSitemap

© 2026 AiFeed24. All rights reserved.

Affiliate disclosure: We earn commissions on qualifying purchases. Learn more

#cybersecurity
#funding
#apple
#google
#microsoft
#llm
#fintech
#saas