Claude Fable 5's Router: Paranoia or Performance Shift?
Did Claude Fable 5 get dumber? Two benchmarks, two wildly different conclusions—and one routing layer that explains the whole mess.
Topic
31 articles found
Did Claude Fable 5 get dumber? Two benchmarks, two wildly different conclusions—and one routing layer that explains the whole mess.
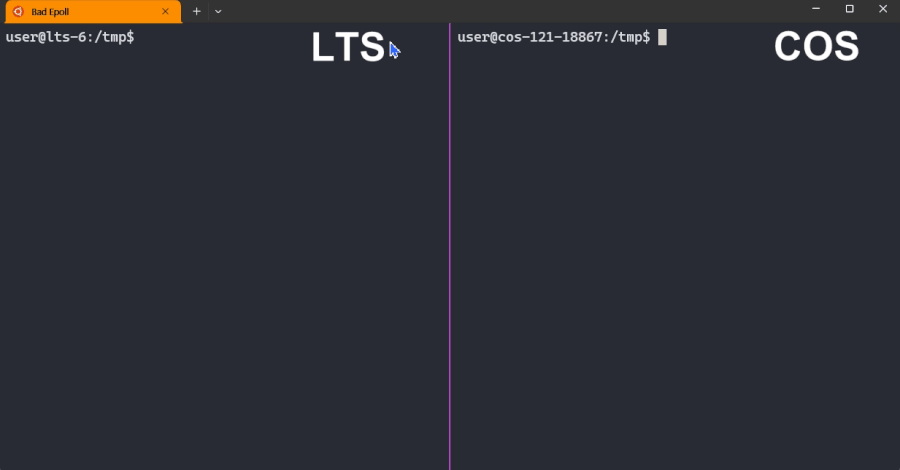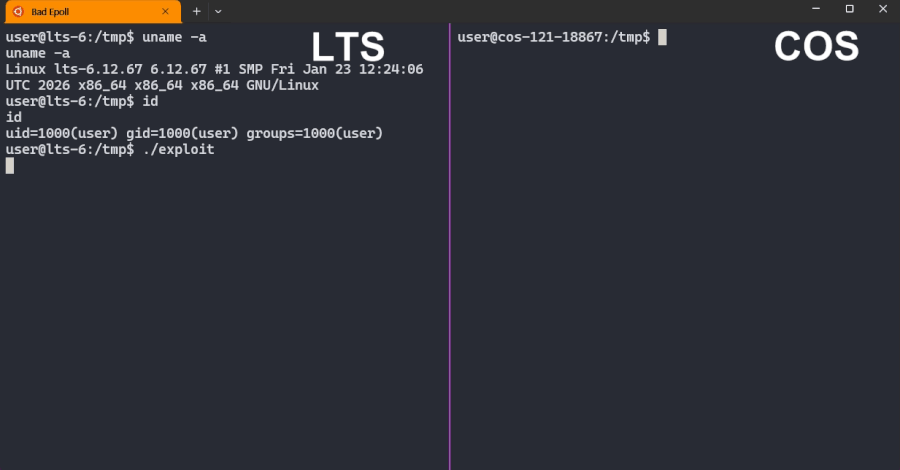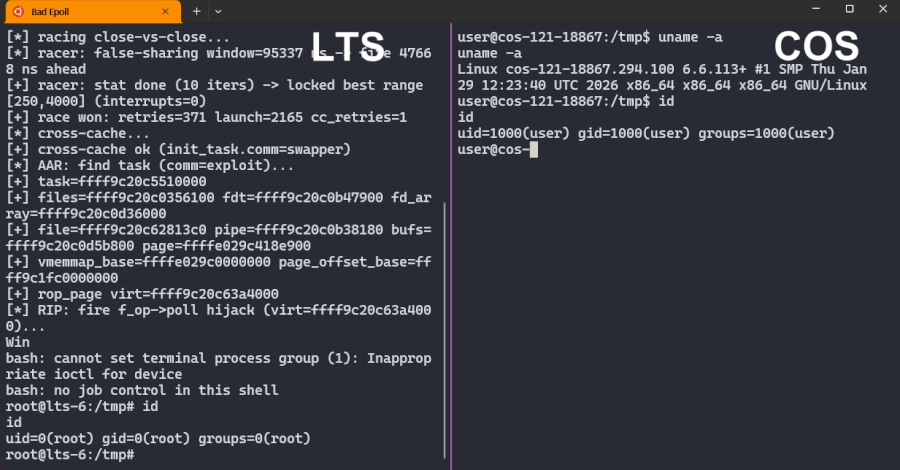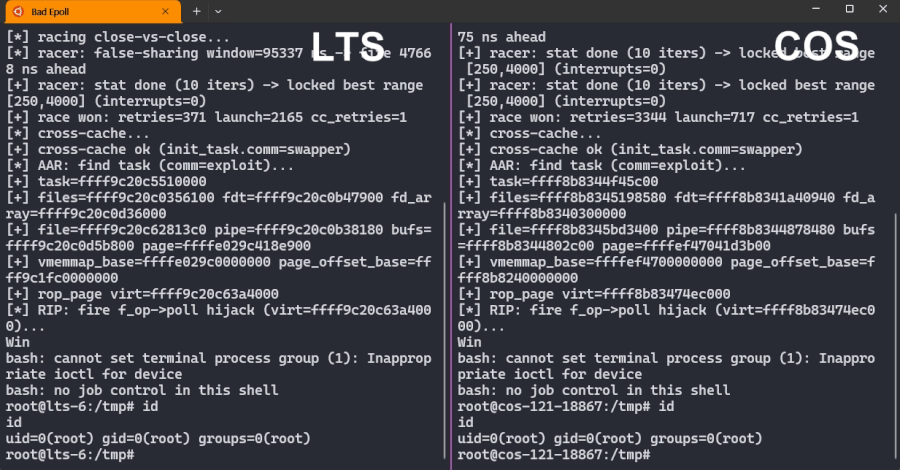
A newly disclosed Linux kernel flaw called Bad Epoll (CVE-2026-46242) lets an ordinary user with no special access take full control of a machine as root. It affects Linux desktops, servers, and Android, and a fix is out. Bad Epoll sits in the same small stretch of kernel code where Anthropic's most
Researchers say a new jailbreak technique tricked AI models into treating attacker-written text as their own reasoning, bypassing safety guardrails and exposing a deeper security flaw.
IBM and Red Hat assign 20,000 engineers to the new Project Lightwell service as Anthropic's Mythos findings ignite debate over how to secure the open-source software supply chain.
The rebuttal came as part of a set of FAQs released by the Meta-owned messaging platform around its contentious username feature - which is under fire over impersonation and fraud concerns.
If you tend to copy/paste content from websites, you might be surprised to find yourself under the thrall of a ClickFix attack, but Opera has a solution to fix it before you click it.
Microsoft's new Teams admin policy requires organizer approval for external AI bots, giving organizations greater visibility and control over automated participants in sensitive meetings. The post Microsoft Adds New Teams Controls to Block Unauthorized AI Bots From Meetings appeared first on Securit
In January 2021, an attacker added a single line of code to a popular bash script. Tens of thousands of The post The call is coming from inside your pipeline: the anatomy of a Codecov attack appeared first on The New Stack.
Crypto hacks hit $75.9M across 40 incidents in June, down 7.1% from May, led by the $31M Humanity Protocol exploit, PeckShield said.
Logged-out Old Reddit access is “significant source of abusive scraping."
Software updates are rolling out now for iPhone, iPad, and Mac, bringing fixes that weren't supposed to arrive so soon. Here's why.
Microsoft has extended Windows Server 2022 hotpatching until October 2027, one year after the mainstream end date of October 2026. [...]
Claude Mythos has raised concerns about AI-driven attacks on DeFi protocols. However, the same AI tools are also available to security teams, not just attackers.
A niche type of fraud is lucrative enough for criminals to set up fake websites with dodgy software to harvest your data After holding them for a few years, you have decided it is time to cash in your cryptocurrency holdings. The problem is, it is so long since you set up the digital wallet which ma
Rising threats from third-party actors are forcing institutions to play defense to protect student data from ransomware and other attacks.
Deloitte Touche Tohmatsu Ltd. is joining an initiative that IBM Corp. and its Red Hat unit launched in May to fix open-source software vulnerabilities. The companies announced the move today. U.K.-based Deloitte launched in the middle of the 18th century as an accounting firm. Today, it’s the world’
The Open Source Sustainability Initiative's goal is to help enterprises manage and secure aging open source projects while maintaining regulatory compliance.
Polymarket says it will fully reimburse customers who lost an estimated $3 million after hackers injected a malicious script into the platform's frontend following a breach at a third-party vendor. [...]
Cisco joins a growing list of security platform providers who are betting that securing the agentic workforce means turning identity into the primary control plane.
It might be taking a bit longer than usual to respond to your submissions — here's why.